MAST Consulting Group

  • Home
  • Author: MAST Consulting Group
  • Page 2
Regulatory Gap Assessment | Framework & Governance Design | RCSA & KRI Implementation | Critical Operations Mapping | Operational Resilience | BCM & DR | ICT & Cybersecurity Resilience | Third-Party Risk | Regulatory Reporting | Independent Validation & Training.

CBUAE Operational Risk Management Regulation 2026: Are UAE Financial Institutions Ready?

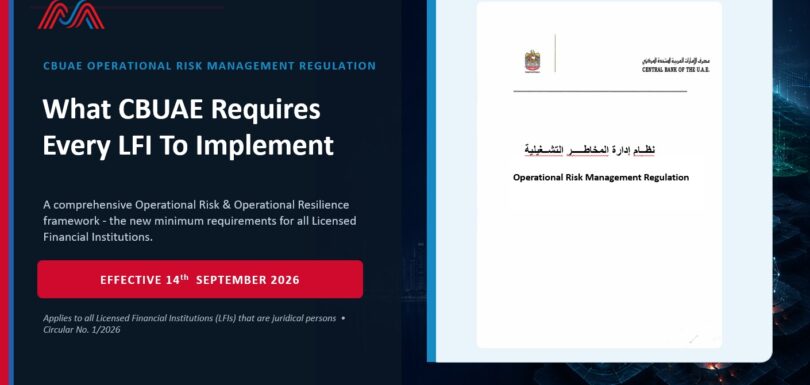
The Central Bank of the UAE (CBUAE) Operational Risk Management Regulation – Circular No. 1/2026 introduces enhanced requirements for Licensed Financial Institutions (LFIs) to establish a comprehensive Operational Risk and Operational Resilience framework. The regulation becomes effective on 14 September 2026. For LFIs, this means moving beyond traditional risk management and ensuring that operational resilience […]
Continue Reading
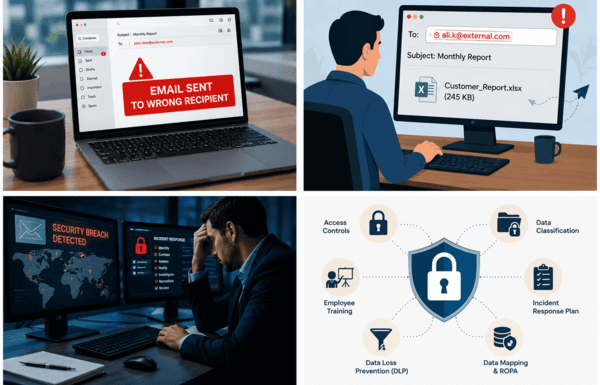
UAE PDPL Compliance: What Happens When Personal Data Goes Wrong? UAE Personal Data Protection Law (PDPL)

UAE PDPL Compliance: What Happens When Personal Data Goes Wrong?

Organizations process significant volumes of personal data every day, including customer names, contact details, Emirates ID information, financial records, and employee data. A personal data breach does not always result from a cyberattack. Sometimes, a simple operational error—such as sending an email to the wrong recipient—can create a serious privacy incident. Let’s look at a […]
Continue Reading
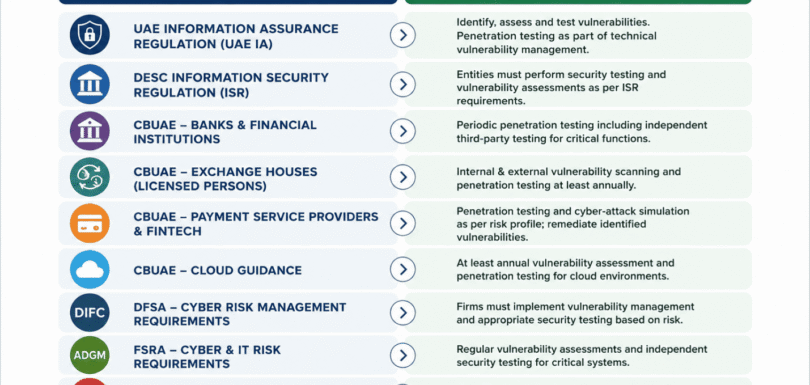
VAPT Services in UAE: Protect Your Business & Meet Regulatory Requirements.

VAPT Services in UAE: Regulatory Requirements, Compliance & Security Testing

As UAE organizations accelerate digital transformation, cloud adoption, and online services, cybersecurity risks continue to increase. A single vulnerability in a network, application, API, or cloud environment can lead to data breaches, financial loss, operational disruption, and regulatory non-compliance. Vulnerability Assessment and Penetration Testing (VAPT) helps organizations identify and validate security weaknesses before attackers can […]
Continue Reading
ISO/IEC 42001 Artificial Intelligence Management Systems (AIMS) Consulting Services in UAE, Dubai, Abu Dhabi , Saudi Arabia, Top ISO 42001 Consulting Company in Middle East

ISO/IEC 42001: Why AI Governance Matters More Than Ever

Artificial Intelligence (AI) is transforming the way businesses operate. From automating customer service to improving healthcare diagnostics and strengthening fraud detection, AI is helping organizations become more efficient and innovative. However, as AI adoption grows, so do the risks associated with bias, privacy, security, and accountability. This is where ISO/IEC 42001, the world’s first international […]
Continue Reading
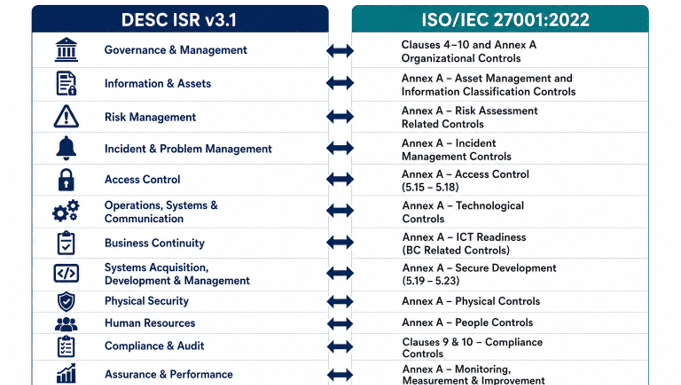
DESC ISR compliance, ISO 27001 to DESC ISR mapping, Cybersecurity compliance UAE

DESC ISR: What It Is, Who Must Comply, and How It Maps to ISO 27001

Dubai’s cybersecurity landscape is evolving rapidly, and organizations operating within the emirate’s government ecosystem are expected to keep pace. The Dubai Electronic Security Centre (DESC)  Dubai’s dedicated cybersecurity authority enforces the Information Security Regulation (ISR v3.1), a comprehensive thirteen-domain framework that sets the mandatory baseline for information security governance, risk management, and control implementation across […]
Continue Reading
AI GRC Implementation Framework, Responsible AI Governance Model AI Security and Compliance Framework

AI GRC Implementation Checklist: A Complete Guide to AI Governance, Risk Management & Compliance

Artificial Intelligence (AI) is no longer an emerging technology—it is now a strategic business enabler. Organizations across finance, healthcare, retail, manufacturing, government, and technology sectors are integrating AI into business operations to automate processes, enhance customer experiences, improve decision-making, and drive innovation. However, successful AI adoption extends beyond deploying powerful models. Organizations must establish effective […]
Continue Reading