CB UAE Compliance

CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE

CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE. (Part 1)

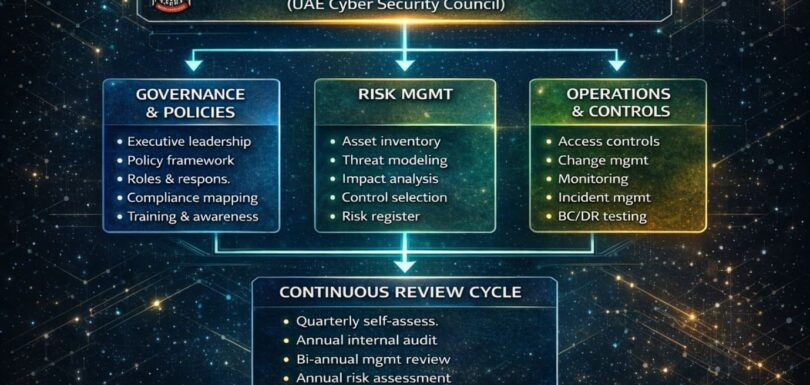
Cybersecurity, GRC, Operational Risk and Operational Resilience Requirements Banks and Licensed Financial Institutions (LFIs) operating in the UAE are subject to a comprehensive regulatory framework established by the Central Bank of the UAE (CBUAE). CBUAE requirements address key areas including Governance, Risk and Compliance (GRC), Operational Risk, Operational Resilience, ICT and Cybersecurity, Information Assurance, Internal […]
Continue Reading
Regulatory Gap Assessment | Framework & Governance Design | RCSA & KRI Implementation | Critical Operations Mapping | Operational Resilience | BCM & DR | ICT & Cybersecurity Resilience | Third-Party Risk | Regulatory Reporting | Independent Validation & Training.

CBUAE Operational Risk Management Regulation 2026: Are UAE Financial Institutions Ready?

The Central Bank of the UAE (CBUAE) Operational Risk Management Regulation – Circular No. 1/2026 introduces enhanced requirements for Licensed Financial Institutions (LFIs) to establish a comprehensive Operational Risk and Operational Resilience framework. The regulation becomes effective on 14 September 2026. For LFIs, this means moving beyond traditional risk management and ensuring that operational resilience […]
Continue Reading

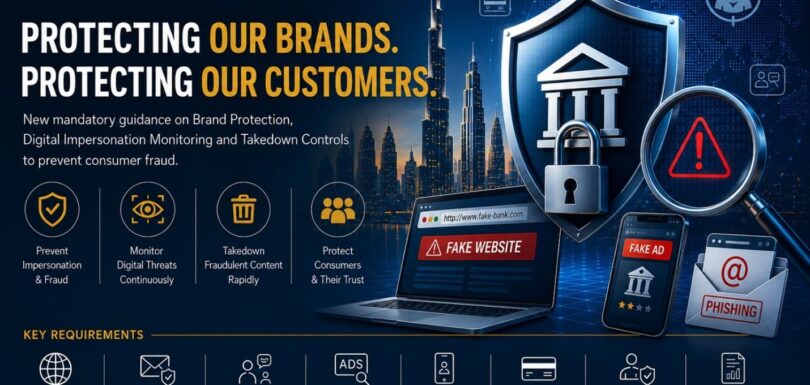
UAE CBUAE Issues mandatory guidance on Brand Protection and Digital Impersonation Monitoring

The Central Bank of the United Arab Emirates (CBUAE) has issued new mandatory guidance requiring all Licensed Financial Institutions (LFIs) in the UAE to strengthen defenses against brand impersonation, phishing, fake advertisements, and digital fraud campaigns targeting consumers. This initiative responds to the increasing misuse of financial institution brands, domains, social media profiles, and communication […]
Continue Reading
ISO 27001 consulting UAE

Beyond VAPT: Why UAE Enterprises Need Continuous Security Governance

Across the UAE, a dangerous assumption persists that a clean Vulnerability Assessment and Penetration Testing (VAPT) report means an organization is secure. This belief is not just misguided it is a direct path to regulatory failure and data breach. This scenario plays out hundreds of times each year across the UAE’s enterprise landscape. And it […]
Continue Reading
Cyberattacks Are Exploding: Is Your Organization Ready? By MAST Consulting Group

Cyber-attacks Are Exploding: Is Your Organization Ready?

Every headline today seems to carry the same message: Cyberattacks are rising… again.From AI-powered phishing scams to destructive malware and supply-chain breaches, organizations in the UAE and across the region are facing a level of cyber risk we’ve never seen before. Remote work has widened the attack surface. AI has supercharged threat actors. And one […]
Continue Reading
CBUAE AI Guidance: A Supervisory Signal for UAE Financial Institutions

CBUAE AI Guidance: A Supervisory Signal for UAE Financial Institutions

The Central Bank of the UAE (CBUAE) issued its Guidance Note on the Consumer Protection and Responsible Adoption and Use of Artificial Intelligence and Machine Learning by Licensed Financial Institutions. Although described as “non-binding”, the Guidance clearly signals that AI governance has entered the supervisory perimeter for UAE financial institutions. CBUAE’s message is clear: Artificial […]
Continue Reading