MAST Consulting Group

  • Home
  • Author: MAST Consulting Group
CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE

CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE. (Part 2)

Cybersecurity Testing, Incident Management, Business Continuity, Outsourcing, Data Protection and Internal Controls In Part 1, we explored four key areas of the CBUAE compliance landscape: Operational Risk Management, Operational Resilience, ICT & Cybersecurity Risk Management, and UAE Information Assurance requirements. In Part 2, we continue with seven additional areas that banks and Licensed Financial Institutions […]
Continue Reading
CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE

CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE. (Part 1)

Cybersecurity, GRC, Operational Risk and Operational Resilience Requirements Banks and Licensed Financial Institutions (LFIs) operating in the UAE are subject to a comprehensive regulatory framework established by the Central Bank of the UAE (CBUAE). CBUAE requirements address key areas including Governance, Risk and Compliance (GRC), Operational Risk, Operational Resilience, ICT and Cybersecurity, Information Assurance, Internal […]
Continue Reading
ADGM Cyber Risk Management Framework 2026

ADGM Cyber Risk Management Framework 2026: What Financial Institutions Need to Know.

Cyber threats continue to increase across the financial sector as institutions become more dependent on digital platforms, cloud services, third-party technology providers and interconnected systems. To strengthen cyber resilience within Abu Dhabi Global Market (ADGM), the Financial Services Regulatory Authority (FSRA) introduced new Cyber Risk Management Rules for Authorised Persons and Recognised Bodies. The requirements […]
Continue Reading
Building a Responsible AI Governance Framework and Achieving ISO/IEC 42001 Certification Readiness

Case Study: ISO/IEC 42001:2023 Implementation for a Saudi Government Organization

Building a Responsible AI Governance Framework and Achieving ISO/IEC 42001 Certification Readiness Client Overview A government organization in the Kingdom of Saudi Arabia was increasingly adopting Artificial Intelligence across its operations and digital services. AI-enabled solutions were being used and evaluated for areas such as data analysis, process automation, decision support, and improving service delivery. […]
Continue Reading
Regulatory Gap Assessment | Framework & Governance Design | RCSA & KRI Implementation | Critical Operations Mapping | Operational Resilience | BCM & DR | ICT & Cybersecurity Resilience | Third-Party Risk | Regulatory Reporting | Independent Validation & Training.

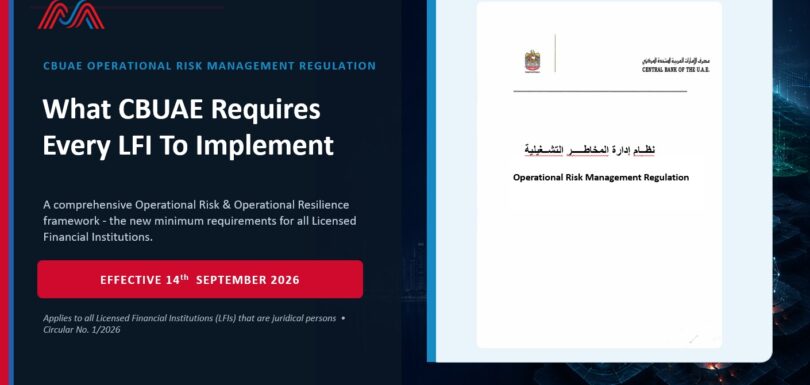
CBUAE Operational Risk Management Regulation 2026: Are UAE Financial Institutions Ready?

The Central Bank of the UAE (CBUAE) Operational Risk Management Regulation – Circular No. 1/2026 introduces enhanced requirements for Licensed Financial Institutions (LFIs) to establish a comprehensive Operational Risk and Operational Resilience framework. The regulation becomes effective on 14 September 2026. For LFIs, this means moving beyond traditional risk management and ensuring that operational resilience […]
Continue Reading
UAE PDPL Compliance: What Happens When Personal Data Goes Wrong? UAE Personal Data Protection Law (PDPL)

UAE PDPL Compliance: What Happens When Personal Data Goes Wrong?

Organizations process significant volumes of personal data every day, including customer names, contact details, Emirates ID information, financial records, and employee data. A personal data breach does not always result from a cyberattack. Sometimes, a simple operational error—such as sending an email to the wrong recipient—can create a serious privacy incident. Let’s look at a […]
Continue Reading