DFSA GEN 5.5: Cyber Risk Management and Compliance Requirements for DIFC Financial Institutions.

DFSA GEN 5.5: Cyber Risk Management and Compliance Requirements for DIFC Financial Institutions.

Introduction As financial institutions increasingly rely on digital technologies, cloud services and interconnected systems, cybersecurity has become a critical regulatory and business priority. The Dubai Financial Services Authority (DFSA) has established cybersecurity requirements under General Module (GEN) Section 5.5 – Cyber Risk Management, aimed at strengthening cyber resilience among regulated financial institutions operating within the […]
Continue Reading
Shadow AI Cybersecurity Risks in UAE Enterprises

Shadow AI in UAE Enterprises: The Hidden Cybersecurity and Compliance Risk

As artificial intelligence transforms business operations across the UAE, a new cybersecurity challenge is emerging: employees using AI tools without organisational approval or oversight Artificial Intelligence (AI) is becoming an essential part of modern business operations. From drafting emails and analysing documents to developing software and automating workflows, AI tools are helping employees improve productivity […]
Continue Reading
VARA Compliance Consulting in Dubai: Helping Virtual Asset Businesses Meet Regulatory Requirements.

VARA Compliance Consulting in Dubai: Helping Virtual Asset Businesses Meet Regulatory Requirements.

Understanding VARA Regulations in Dubai Dubai has established a regulatory framework to support the responsible growth of the virtual asset industry. The Virtual Assets Regulatory Authority (VARA) regulates virtual asset activities in Dubai, excluding the Dubai International Financial Centre (DIFC). Businesses conducting regulated virtual asset activities may need to obtain the appropriate VARA licence before […]
Continue Reading
CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE

CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE. (Part 2)

Cybersecurity Testing, Incident Management, Business Continuity, Outsourcing, Data Protection and Internal Controls In Part 1, we explored four key areas of the CBUAE compliance landscape: Operational Risk Management, Operational Resilience, ICT & Cybersecurity Risk Management, and UAE Information Assurance requirements. In Part 2, we continue with seven additional areas that banks and Licensed Financial Institutions […]
Continue Reading
CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE

CBUAE Compliance Requirements for Banks and Licensed Financial Institutions in the UAE. (Part 1)

Cybersecurity, GRC, Operational Risk and Operational Resilience Requirements Banks and Licensed Financial Institutions (LFIs) operating in the UAE are subject to a comprehensive regulatory framework established by the Central Bank of the UAE (CBUAE). CBUAE requirements address key areas including Governance, Risk and Compliance (GRC), Operational Risk, Operational Resilience, ICT and Cybersecurity, Information Assurance, Internal […]
Continue Reading
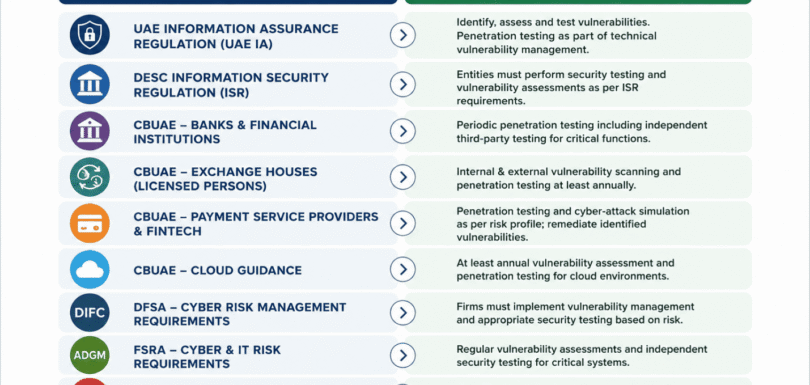
VAPT Services in UAE: Protect Your Business & Meet Regulatory Requirements.

VAPT Services in UAE: Regulatory Requirements, Compliance & Security Testing

As UAE organizations accelerate digital transformation, cloud adoption, and online services, cybersecurity risks continue to increase. A single vulnerability in a network, application, API, or cloud environment can lead to data breaches, financial loss, operational disruption, and regulatory non-compliance. Vulnerability Assessment and Penetration Testing (VAPT) helps organizations identify and validate security weaknesses before attackers can […]
Continue Reading